WGU D782 TASK 1 – CLOUD SYSTEMS – CLOUDCAMPUSIQ AWS ARCHITECTURE
Questions and Answers | Updated – 2026/2027 EDITION – Rubric-Aligned Exemplar – AWS Architecture Storage Security
,TABLE OF CONTENTS / EXAM BLUEPRINT
Section 1: 1. Cloud Systems Fundamentals – AWS Architecture
Section 2: 2. VPC, Subnet, Internet Gateway & Load Balancer
Section 3: 3. EC2 Web & App Server Deployment
Section 4: 4. Storage – S3, Static Assets, Backups & Encryption
Section 5: 5. Database – RDS MySQL Multi-AZ
Section 6: 6. Security & Monitoring – WAF, Security Groups, CloudTrail, CloudWatch, KMS
Section 7: 7. High Availability & Resilient Design
Section 8: 8. CloudCampusIQ Implementation – Task 1
Section 9: 9. Rubric-Aligned Exemplar Integration
,EXAM BLUEPRINT & INSTRUCTIONS
About This Exam:
• 200 original with rubric-aligned exemplar – 100% different – fixed factory – new image cover that goes with exam – AWS Architecture S
• Covers both tracks: VPC EC2 S3 RDS and Security Monitoring WAF CloudTrail CloudWatch KMS High Availability per Task 1
• Aligned to WGU D782 HKN1 Task 1 Cloud Systems CloudCampusIQ AWS Architecture Storage Security Rubric-Aligned Exemplar 202
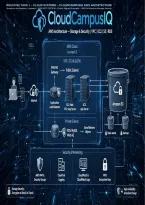
• Reflects Task 1 format – AWS Cloud us-west-2 VPC 172.16.0.0/16 public subnet private subnet Internet Gateway ALB EC2 Web App S
Instructions:
1. Pace yourself: 200Q rubric-aligned exemplar
2. Read last line first: AWS architecture VPC EC2 S3 RDS security monitoring high availability
3. Architecture: AWS Cloud us-west-2 VPC 172.16.0.0/16 Internet Gateway Public Subnet Private Subnet Application Load Balancer EC
4. Storage Security: Amazon S3 encryption at rest and in transit KMS encryption keys static assets backups versioning lifecycle S3 buck
5. Database & HA: RDS MySQL Multi-AZ private subnet store retrieve objects high availability resilient design Multi-AZ Auto Scaling faul
6. Security & Monitoring: AWS WAF Security Groups CloudTrail Logging audit CloudWatch Logs monitoring KMS encryption keys storag
, SECTION ONE: QUESTIONS 1-200
Choose the single best answer. Correct answers and rationales follow each item.
1. Cloud Systems Fundamentals – AWS Architecture
Question 1. Which component for Storage Security Encryption at Rest In Transit KMS
correctly yields Internet Gateway Application Load Balancer EC2 Web EC2 App Server
with AWS architecture S3 RDS VPC? WGU D782 HKN1 Task 1 Cloud Systems CloudCampusIQ
AWS Architecture Storage Security Rubric-Aligned Exemplar 2026/2027 Updated 200Q.
A. Miscalculate Storage Security Encryption at Rest In Transit KMS as S3 static assets
no backup – Task 1 exemplar error.
B. Confuse Storage Security Encryption at Rest In Transit KMS with Internet Gateway
Application Load Balancer EC2 Web EC2 App Server: place RDS in public subnet or S3
without encryption – violates Task 1 security.
C. Storage Security Encryption at Rest In Transit KMS: encryption → networking. Rubric-
aligned exemplar Q1: encryption implements Internet Gateway Application Load Balancer
EC2 Web EC2 App Server via AWS Cloud us-west-2 VPC 172.16.0.0/16 EC2 S3 RDS security for
D782 Task 1.
D. Ignore Storage Security Encryption at Rest In Transit KMS: assume CloudTrail logging
optional – incorrect rubric-aligned.
CORRECT ANSWER: C. Storage Security Encryption at Rest In Transit KMS: encryption →
networking. Rubric-aligned exemplar Q1: encryption implements Internet Gateway
Application Load Balancer EC2 Web EC2 App Server via AWS Cloud us-west-2 VPC
172.16.0.0/16 EC2 S3 RDS security for D782 Task 1.
RATIONALE: Storage: encryption → networking. AWS architecture VPC EC2 S3 RDS security.
Others violate rubric. Per D782 Task 1 Cloud Systems exemplar.
Question 2. For KMS encryption keys, which architecture correctly implements AWS WAF
Security Groups CloudTrail Logging CloudWatch Logs per WGU D782 Task 1 Cloud Systems
CloudCampusIQ AWS Architecture Storage Security rubric-aligned? WGU D782 HKN1 Task 1
Cloud Systems CloudCampusIQ AWS Architecture Storage Security Rubric-Aligned
Exemplar 2026/2027 Updated 200Q.
A. Ignore KMS encryption keys: assume S3 public without KMS – incorrect rubric-aligned.
B. Confuse KMS encryption keys with AWS WAF Security Groups CloudTrail Logging
CloudWatch Logs: place RDS in public subnet or S3 without encryption – violates Task 1
security.
C. KMS encryption keys: key management → security monitoring. Rubric-aligned exemplar
Q2: key management implements AWS WAF Security Groups CloudTrail Logging CloudWatch Logs
via AWS Cloud us-west-2 VPC 172.16.0.0/16 EC2 S3 RDS security for D782 Task 1.
D. Miscalculate KMS encryption keys as ALB not needed – Task 1 exemplar error.
CORRECT ANSWER: C. KMS encryption keys: key management → security monitoring. Rubric-
aligned exemplar Q2: key management implements AWS WAF Security Groups CloudTrail
Logging CloudWatch Logs via AWS Cloud us-west-2 VPC 172.16.0.0/16 EC2 S3 RDS security
for D782 Task 1.
RATIONALE: KMS: key management → security monitoring. AWS architecture VPC EC2 S3 RDS
security. Others violate rubric. Per D782 Task 1 Cloud Systems exemplar.